SBOM · License (Components and Licenses)
An SBOM (Software Bill of Materials) is a bill of materials for software: a complete list of every open-source component and version included in your code.
If you do not know what is inside, you cannot know what is at risk. Modern applications contain far more borrowed open source than hand-written code, and that open source pulls in still more open source. The SBOM organizes this entire makeup into a single inventory.
This analysis generates that component list and, alongside it, evaluates the license risk of each component. For the Source Code service, it is generated automatically from dependencies.
- Analysis : Component inventory (SBOM) and license risk
- What you need : Dependencies of a Source Code service
- Results : SBOM (CycloneDX / SPDX) plus sorting by license risk
SBOMs of other targets are covered in the following documents.
- Container images : Image SBOM
- SBOM files you have already built : SBOM upload
- Java build artifacts : Binary file
What it finds
- Full component inventory : a complete list of which open source is included and at what version. You choose the output format (CycloneDX or SPDX) when you run the analysis, and download the file from Reports.
- License risk : evaluates each component's license into a risk category.
- Copyleft (for example, GPL, AGPL) : distribution terms are strict, so care is needed for commercial distribution.
- Unknown : components whose license could not be identified.
- Permissive (for example, MIT, Apache-2.0) : generally low risk.
Supported scope
- npm · PyPI · RubyGems · Maven / Gradle · Go · Cargo · Composer · NuGet · pub (Dart) · Swift
Viewing results
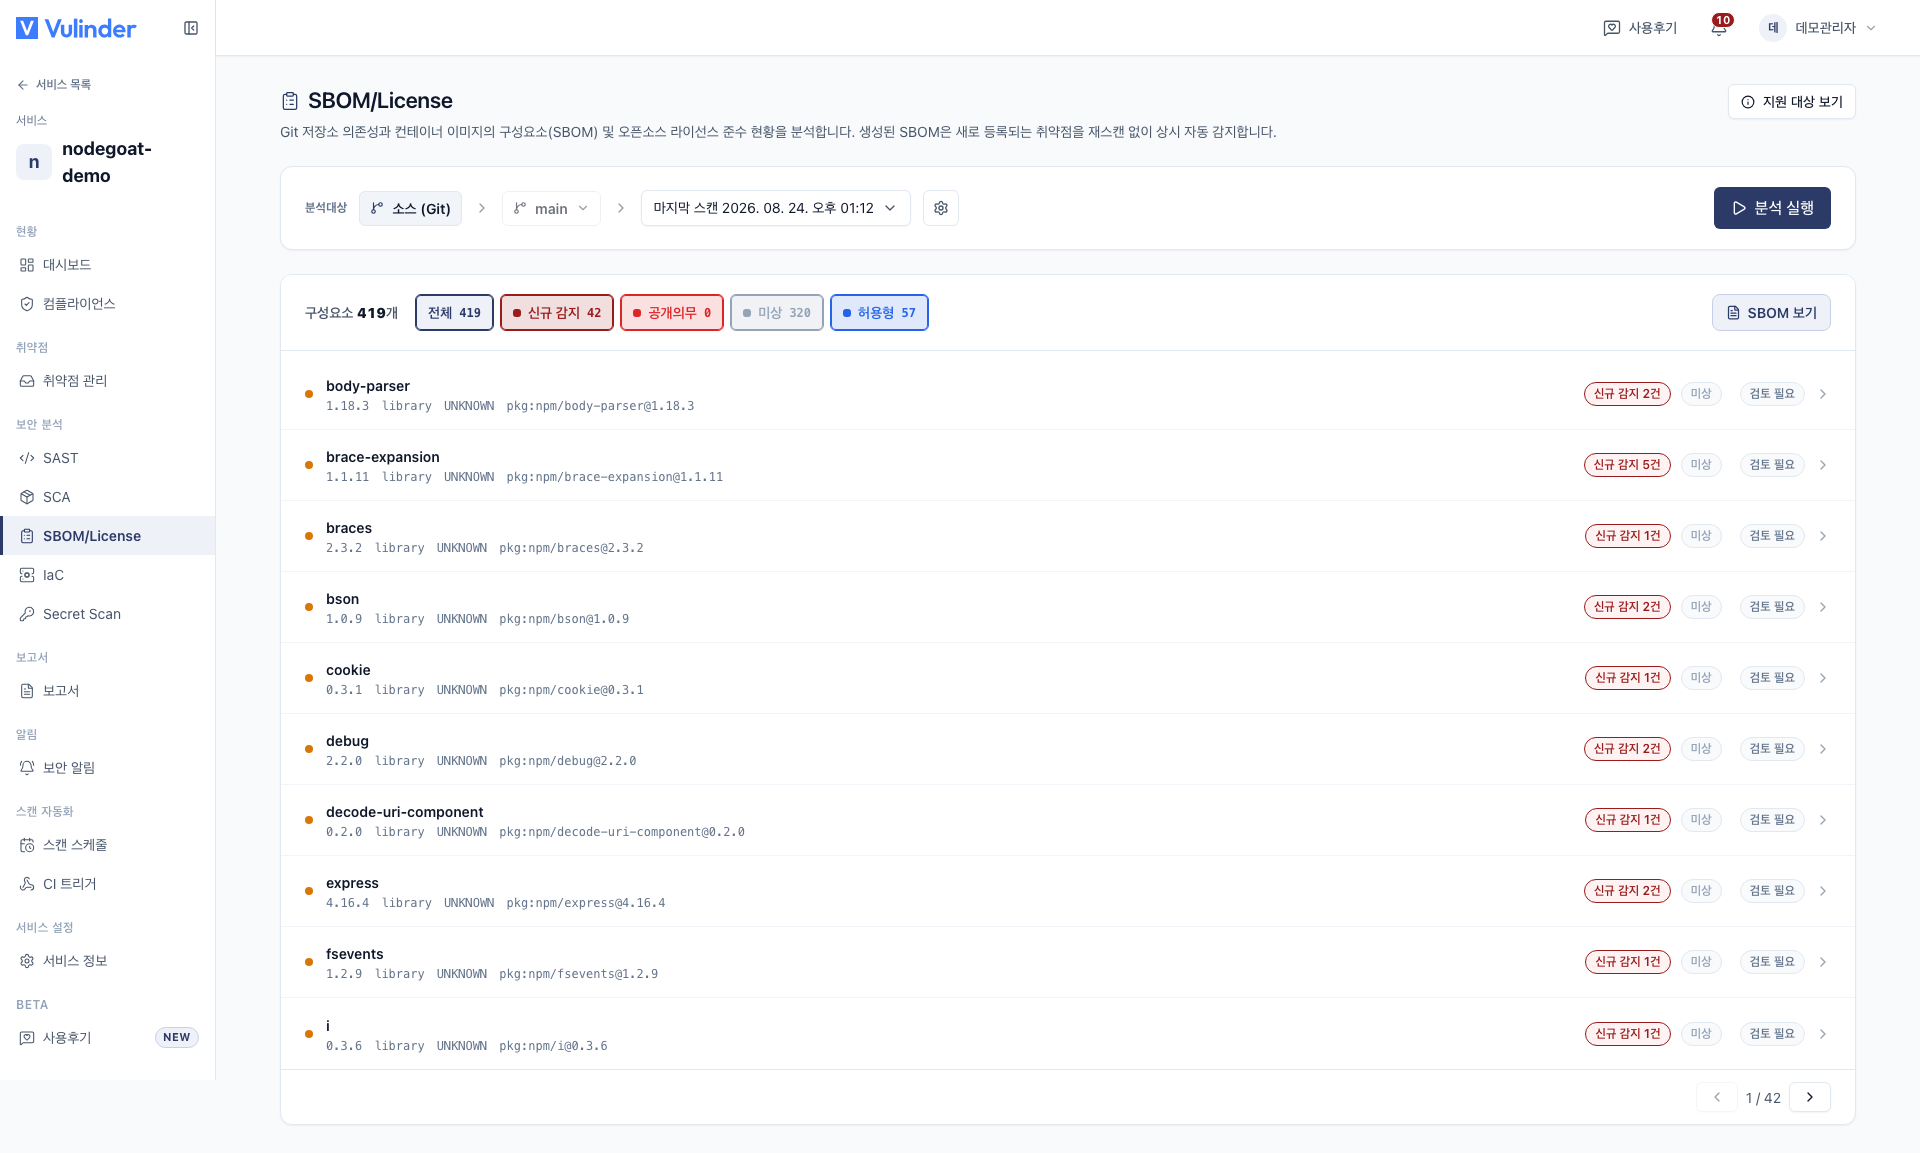
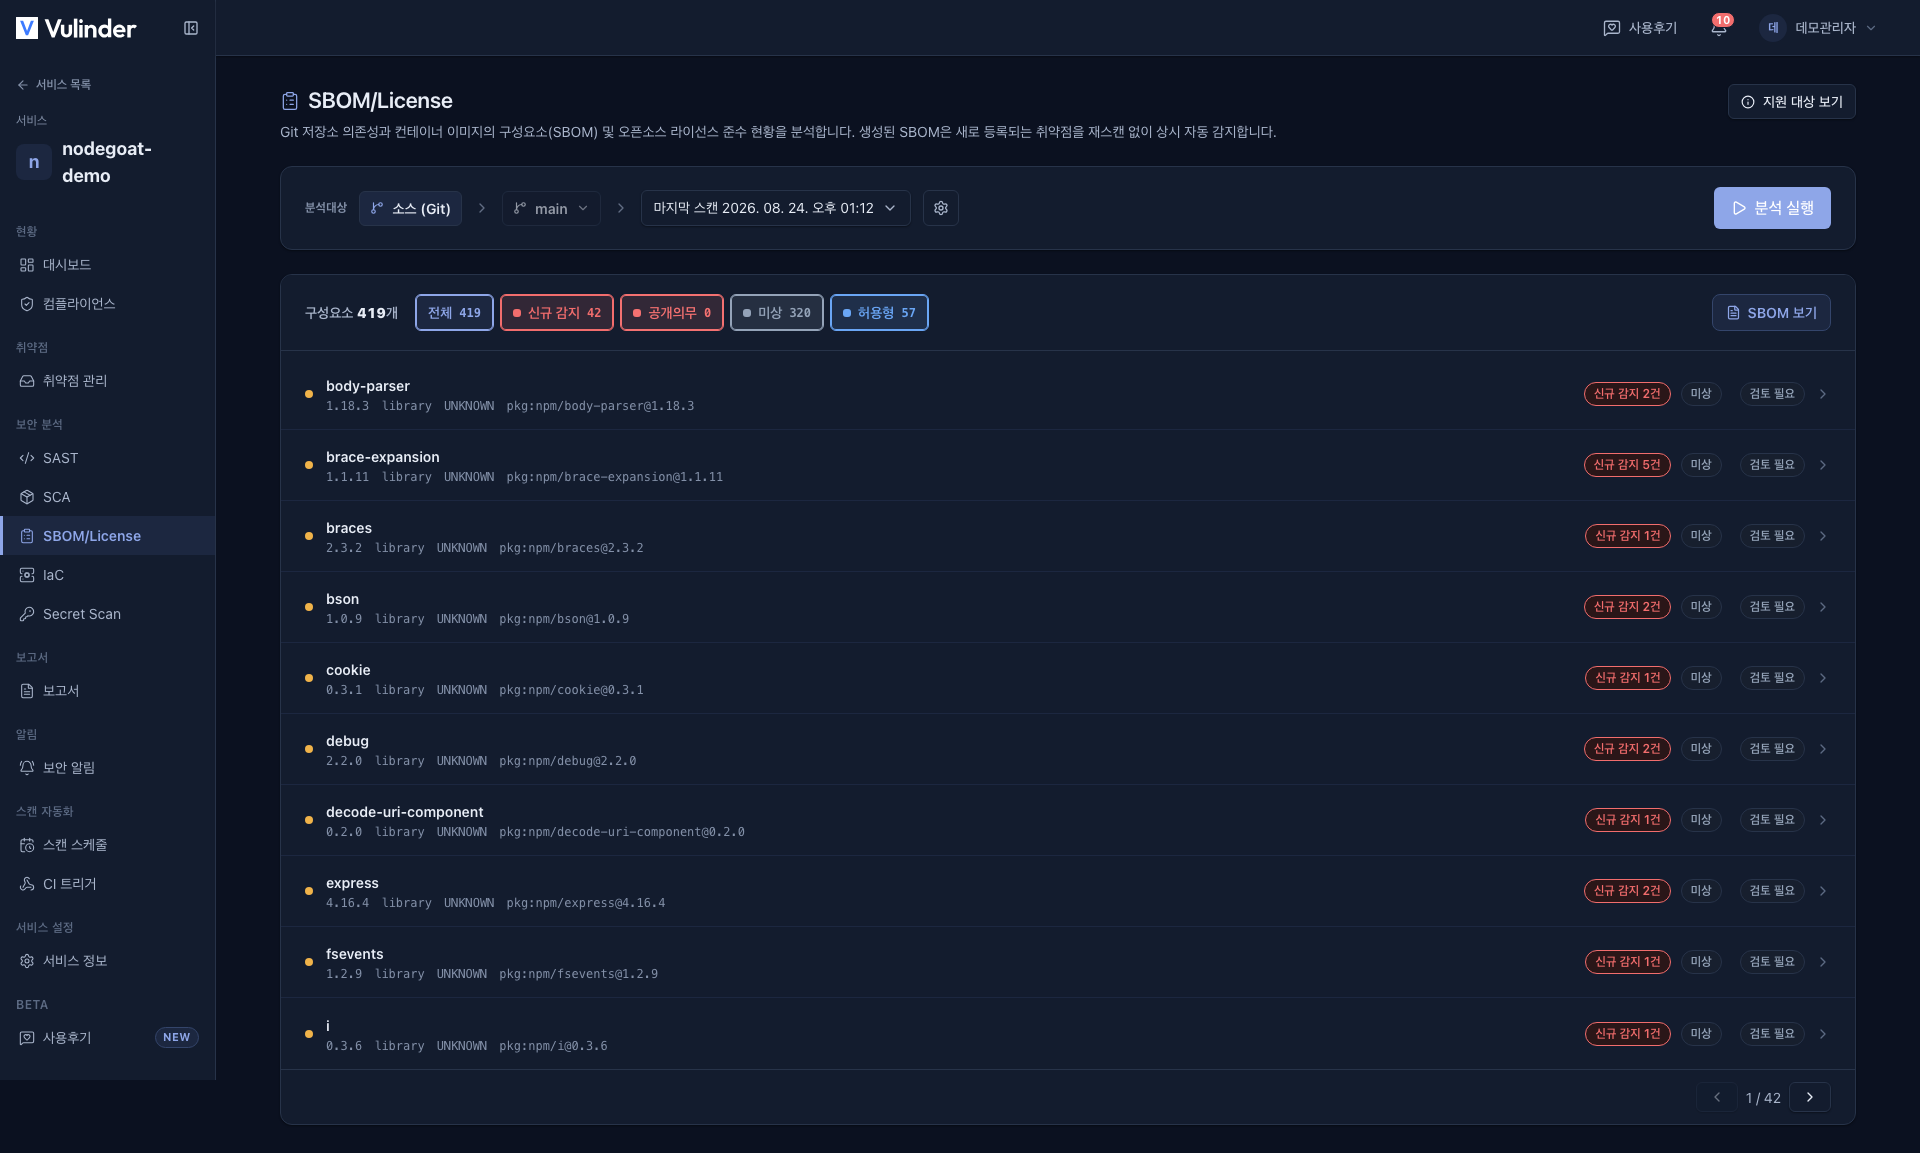
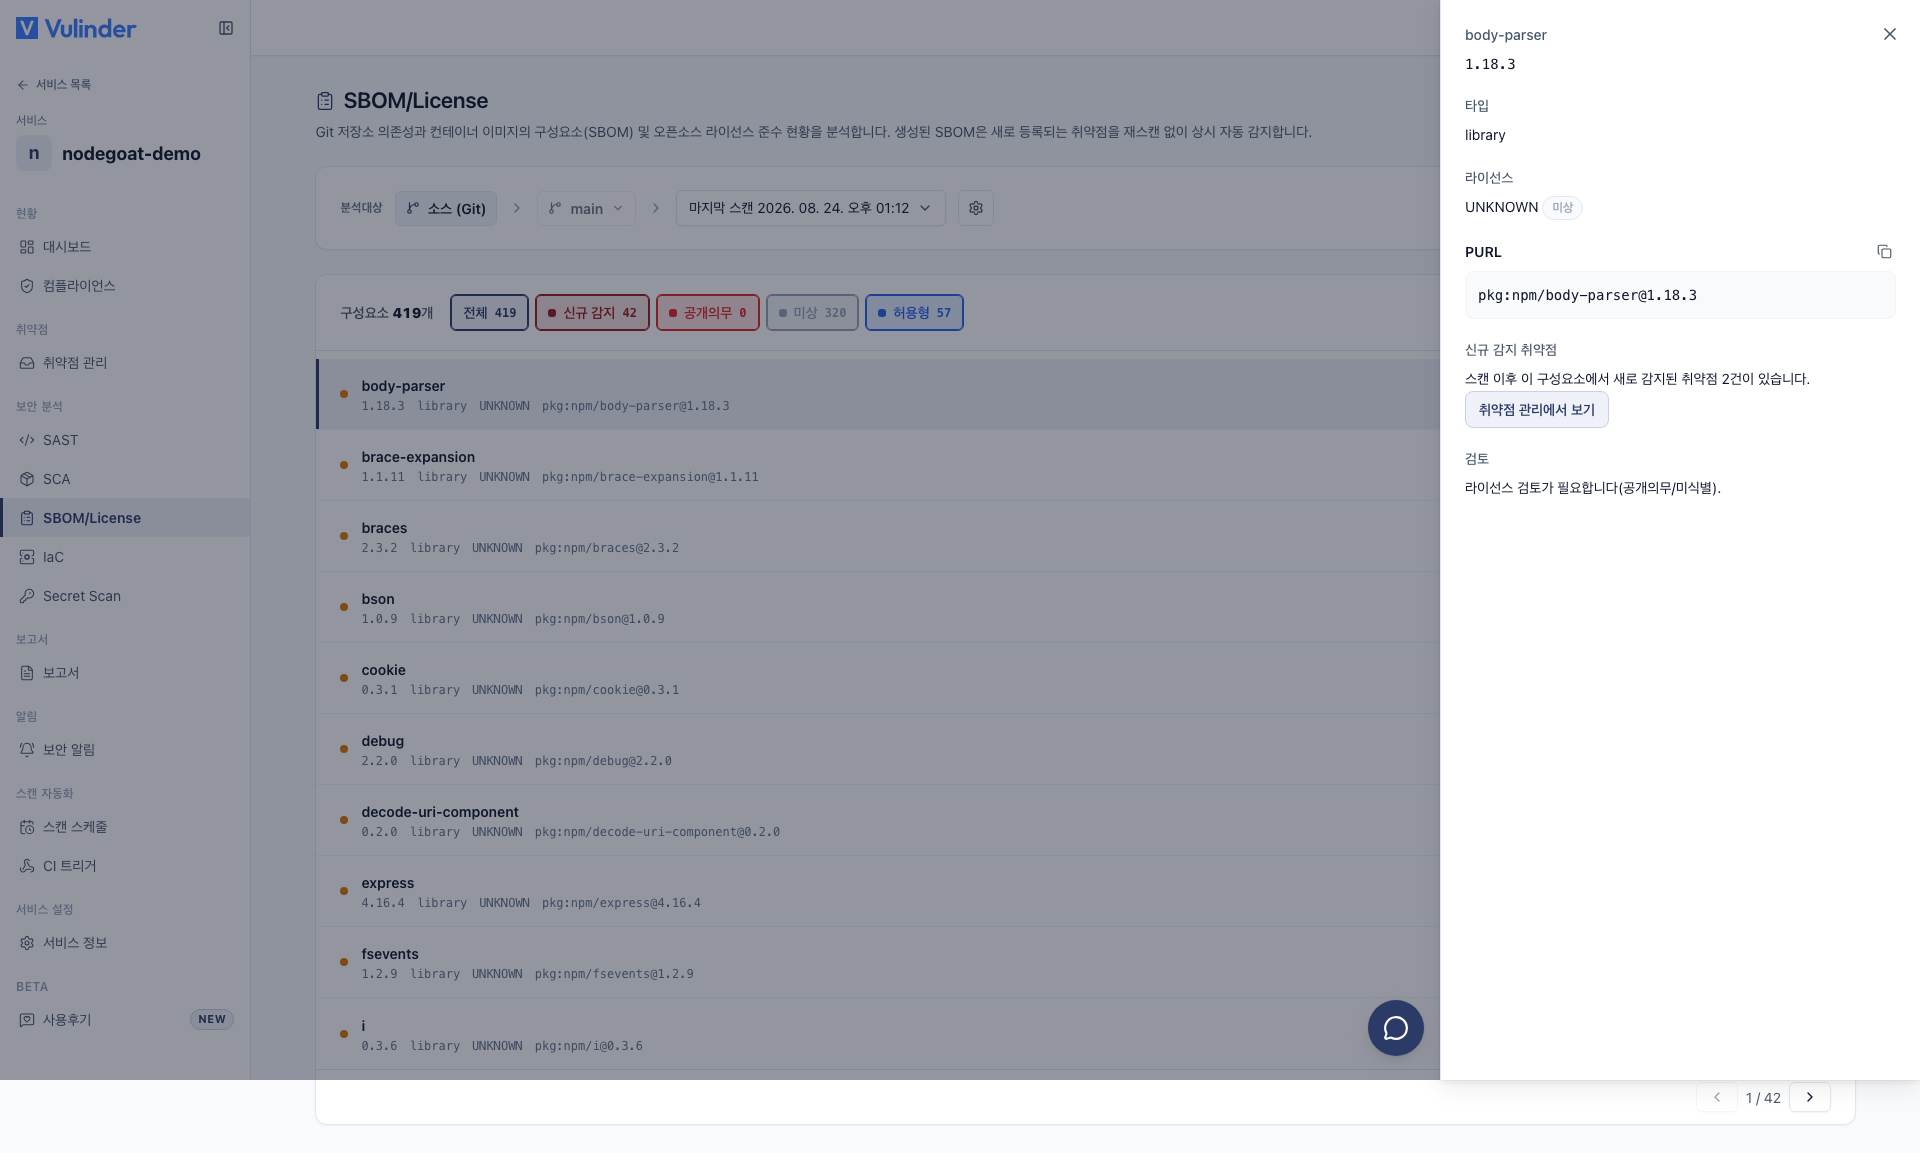
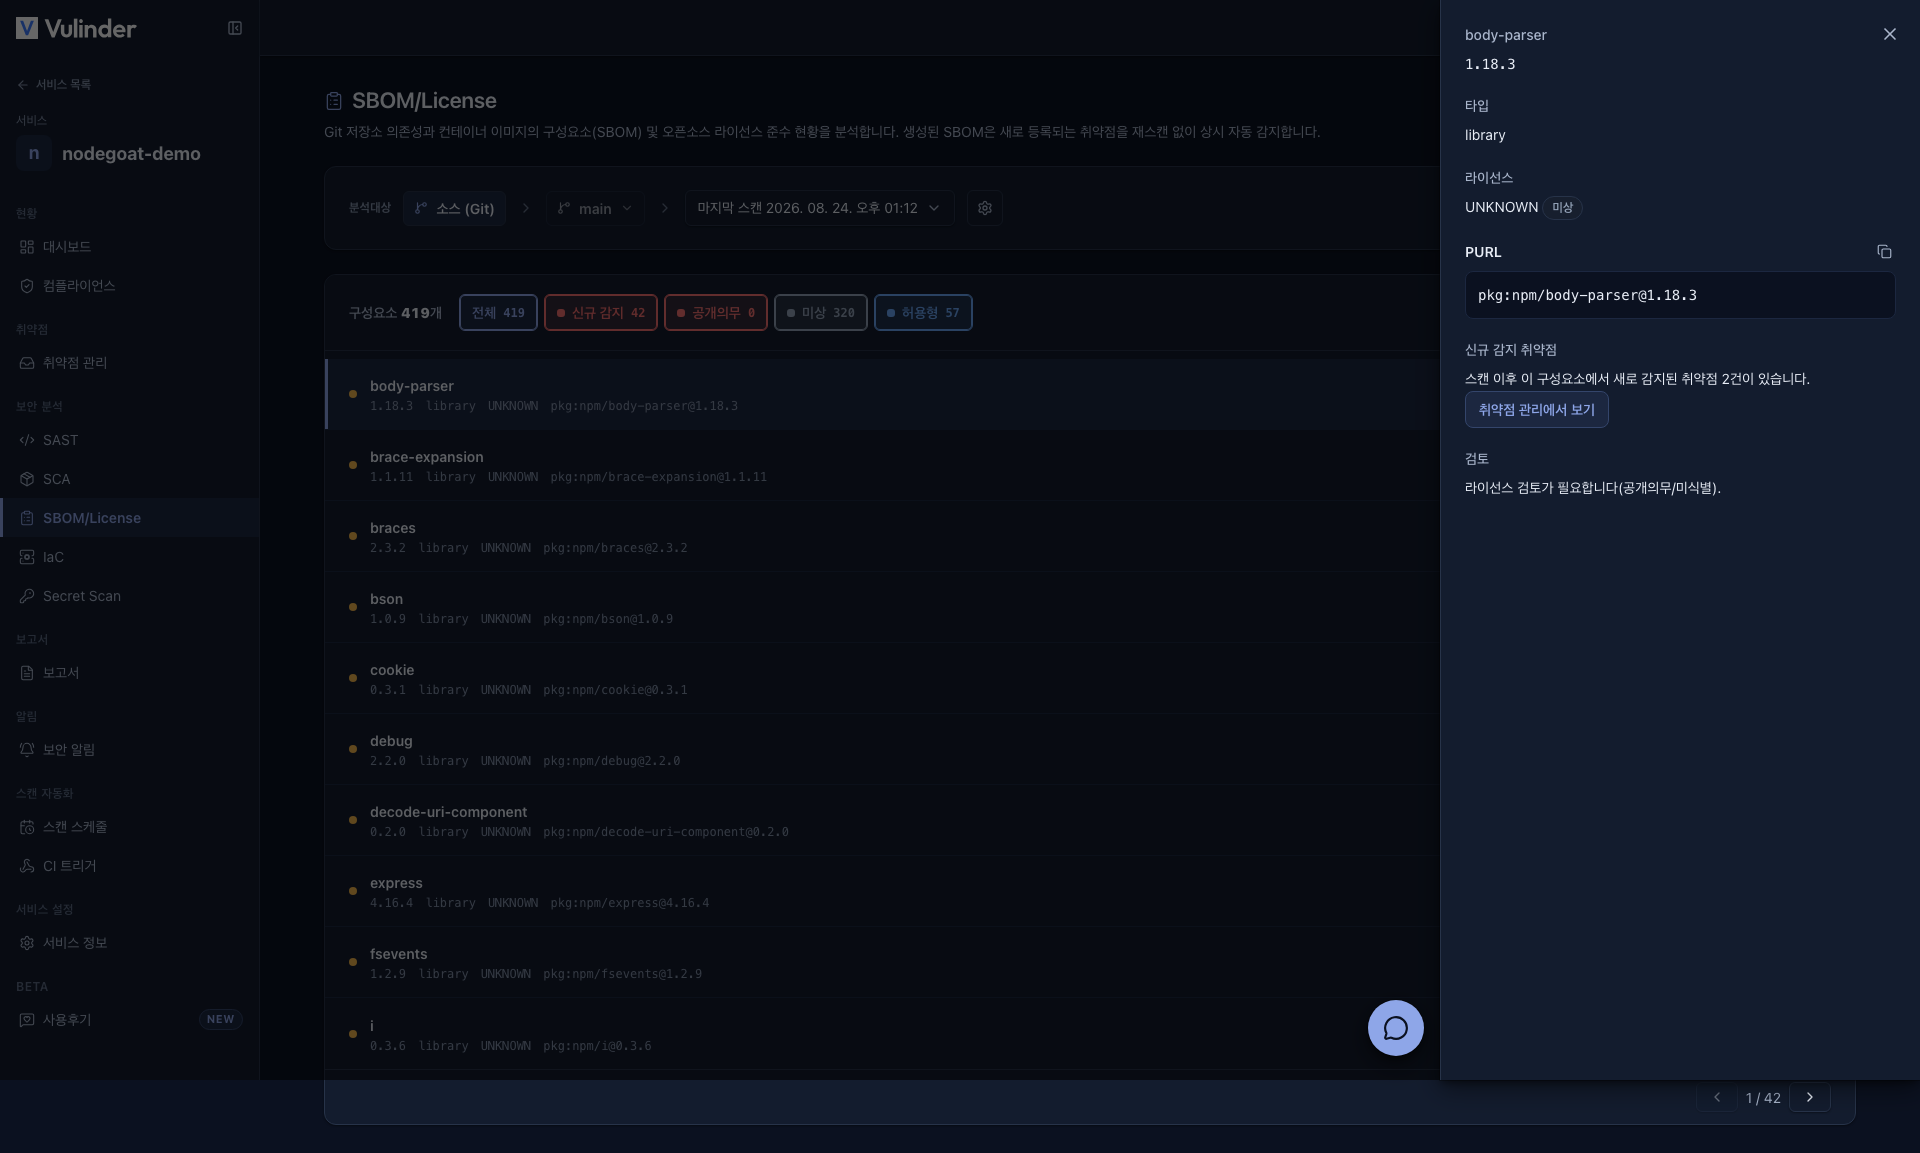
Licenses are not a separate screen: you review them in the component inventory above. Each component in the list shows its license, and clicking a component opens the detail drawer where you can also check it.
The list is sorted in the following order.
- Components with open newly detected vulnerabilities
- License risk from highest to lowest: Copyleft → Unknown → Permissive
Handling results
- License risk is for review only; there is no handling status on components.
- For newly detected vulnerabilities in a component, use View in vulnerability management in the detail panel.
Related documents
- SCA : Check known CVEs in components
- Reports · VEX : Export SBOM / VEX documents
- SBOM upload : Analyze an externally built SBOM