IaC (Infrastructure Code)
Infrastructure as Code (IaC) is the practice of defining infrastructure, such as servers, networks, and clusters, as code using Terraform, Kubernetes manifests, Dockerfiles, and similar formats. Managing it as code is convenient, but it carries the risk that a single bad setting gets deployed and repeated across every environment as-is.
IaC analysis statically inspects these definition files before they are actually applied, catching insecure configuration such as overly open networks or missing encryption before deployment. It targets the infrastructure definition files of the Source Code service.
- Analysis : Infrastructure code (Terraform / K8s / Dockerfile) configuration flaws
- What you need : Infrastructure definition files in the repository
- Results : Findings by severity plus mapping to compliance standards
What it finds
- Overly open networks / security groups
- Missing encryption (at rest / in transit)
- Privileged containers, running as root, missing resource limits
- Hardcoded credentials, insecure defaults
Supported scope
Infrastructure-as-Code scanning supports the following frameworks / formats.
- Terraform · Terraform Plan · CloudFormation · AWS CDK
- Kubernetes · Helm · Kustomize
- Dockerfile · Serverless
- ARM · Bicep (Azure)
- CI pipelines: GitHub Actions · GitLab CI · Bitbucket Pipelines · Azure Pipelines
- Argo Workflows · Ansible · OpenAPI
Viewing results
When a scan finishes, the misconfigurations it found are organized by severity.
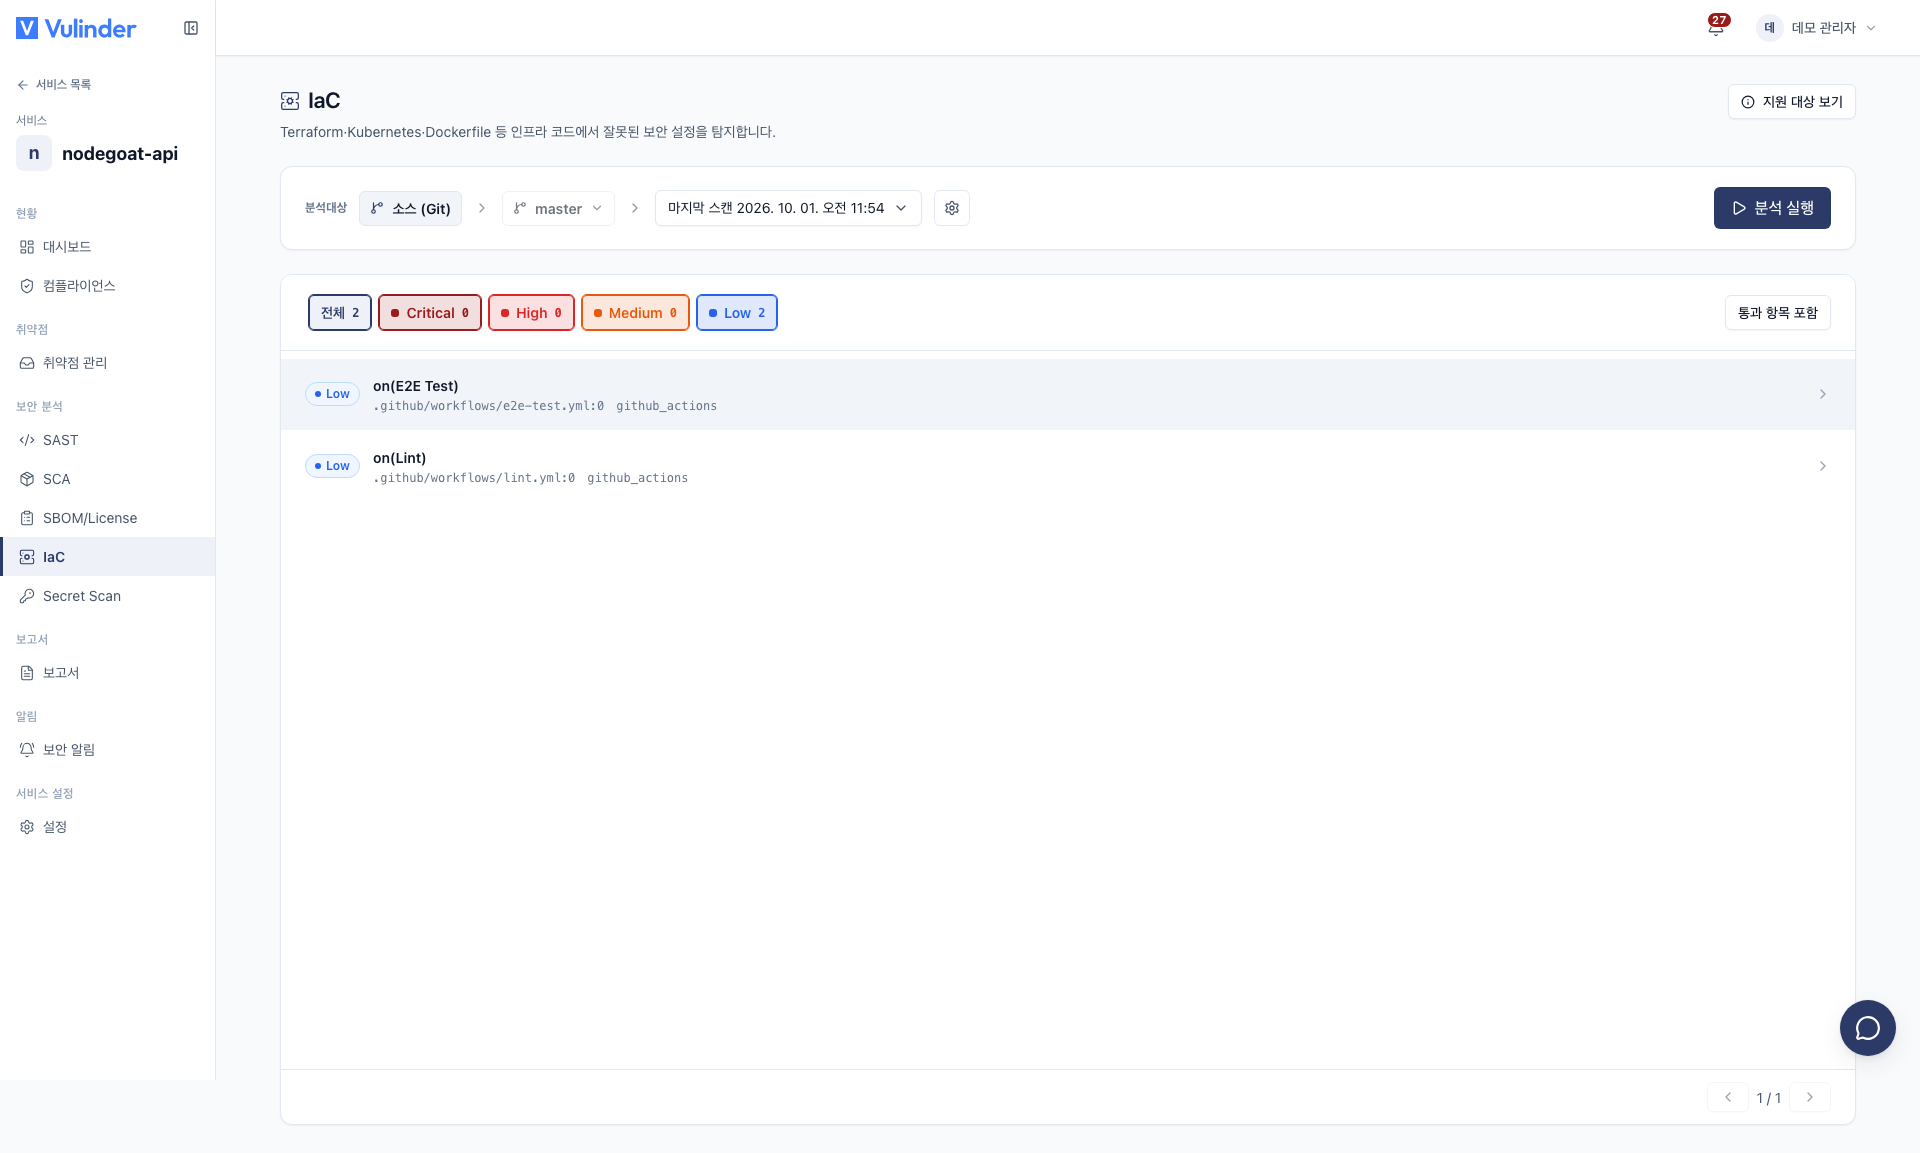
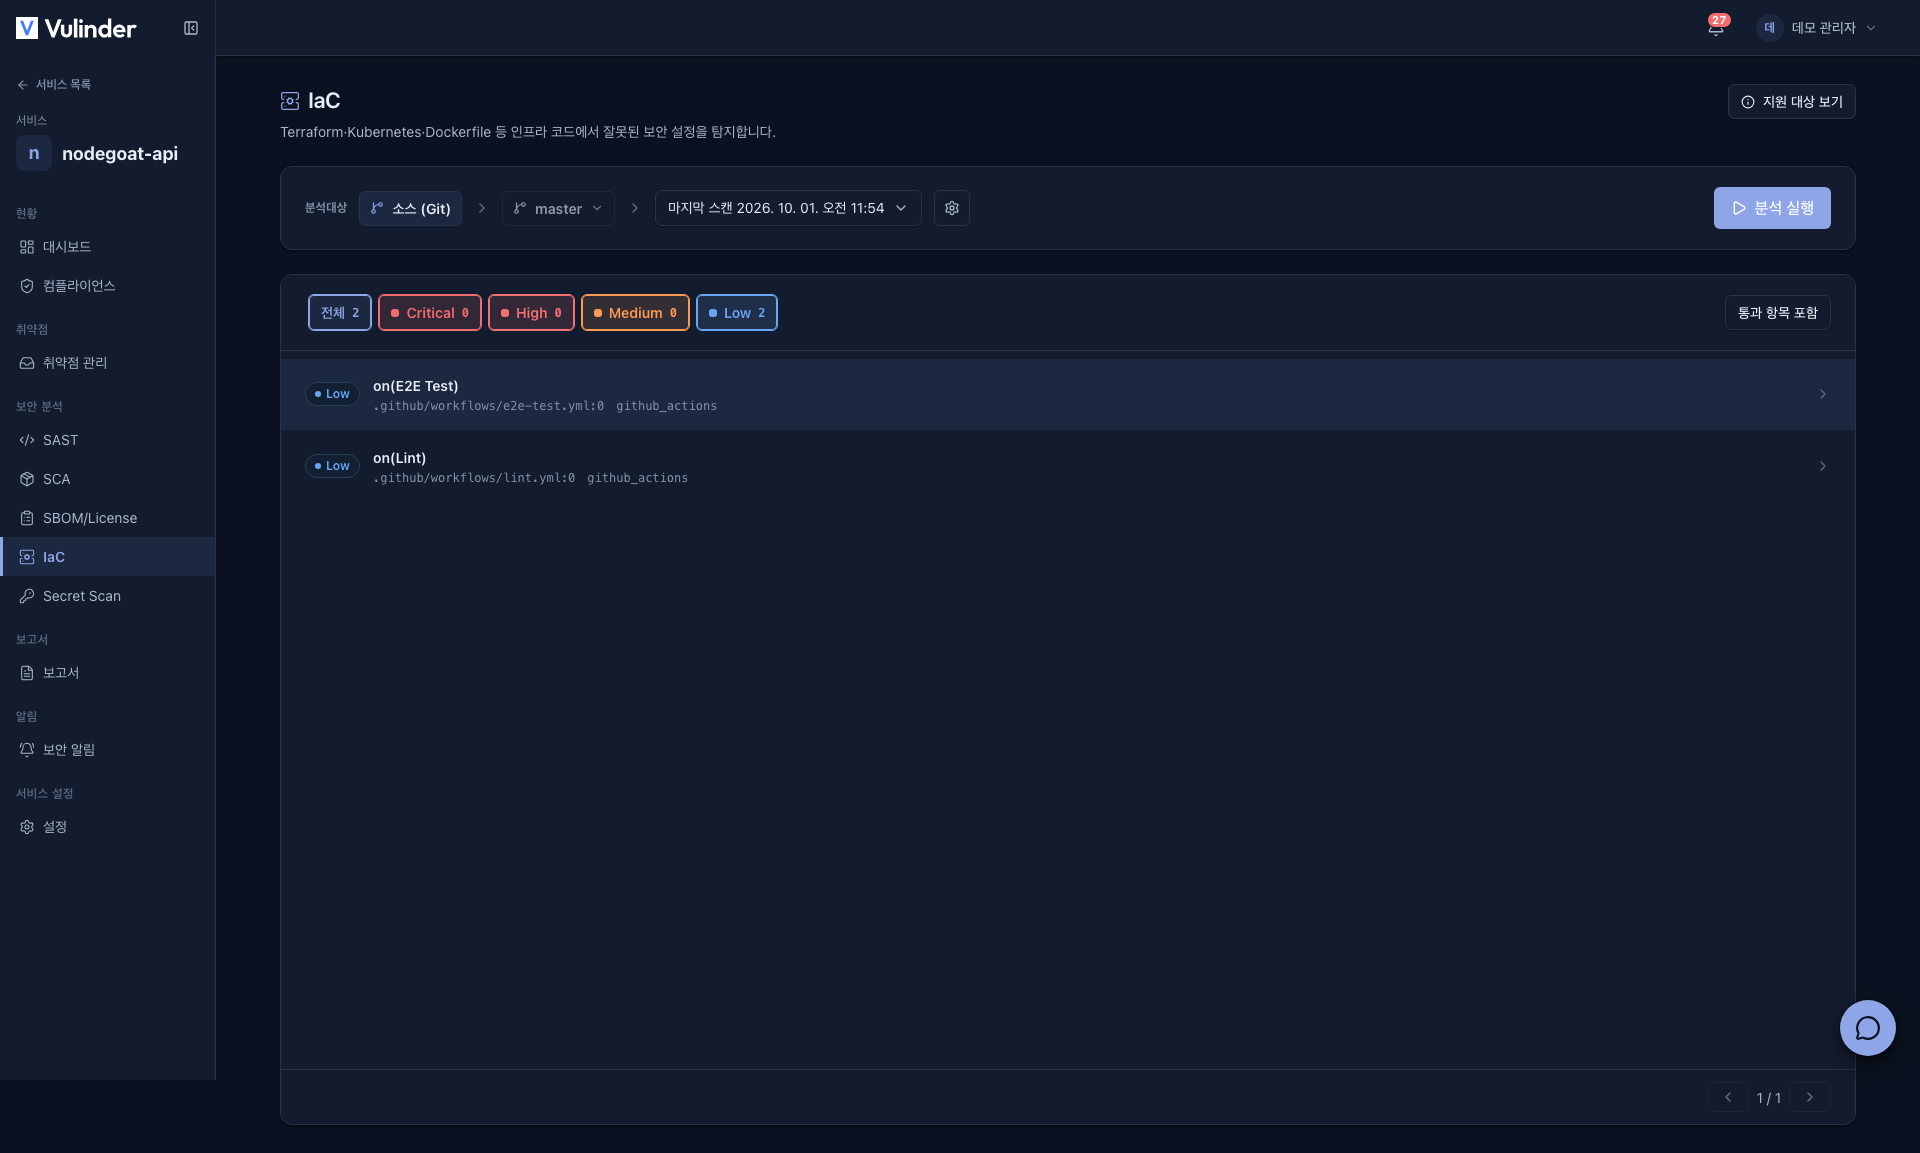
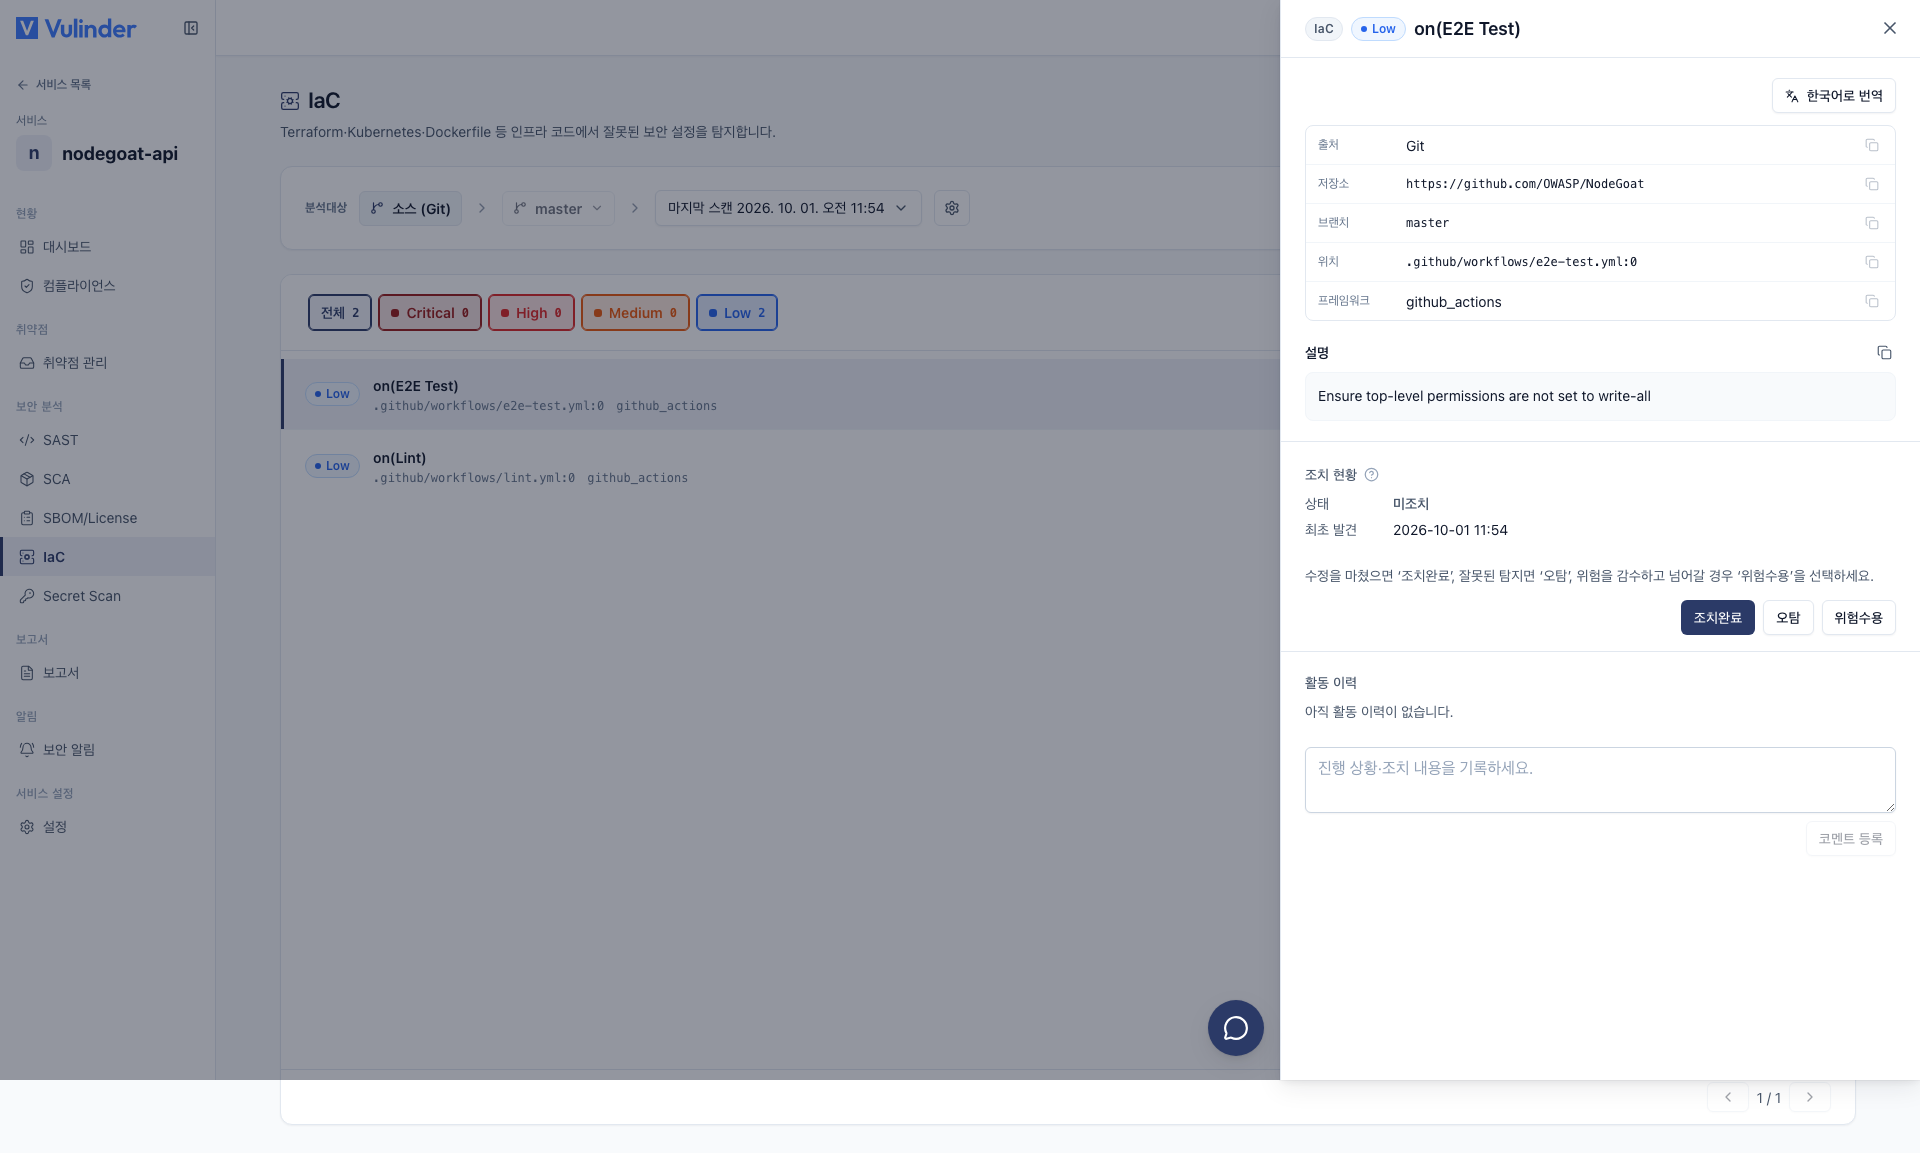
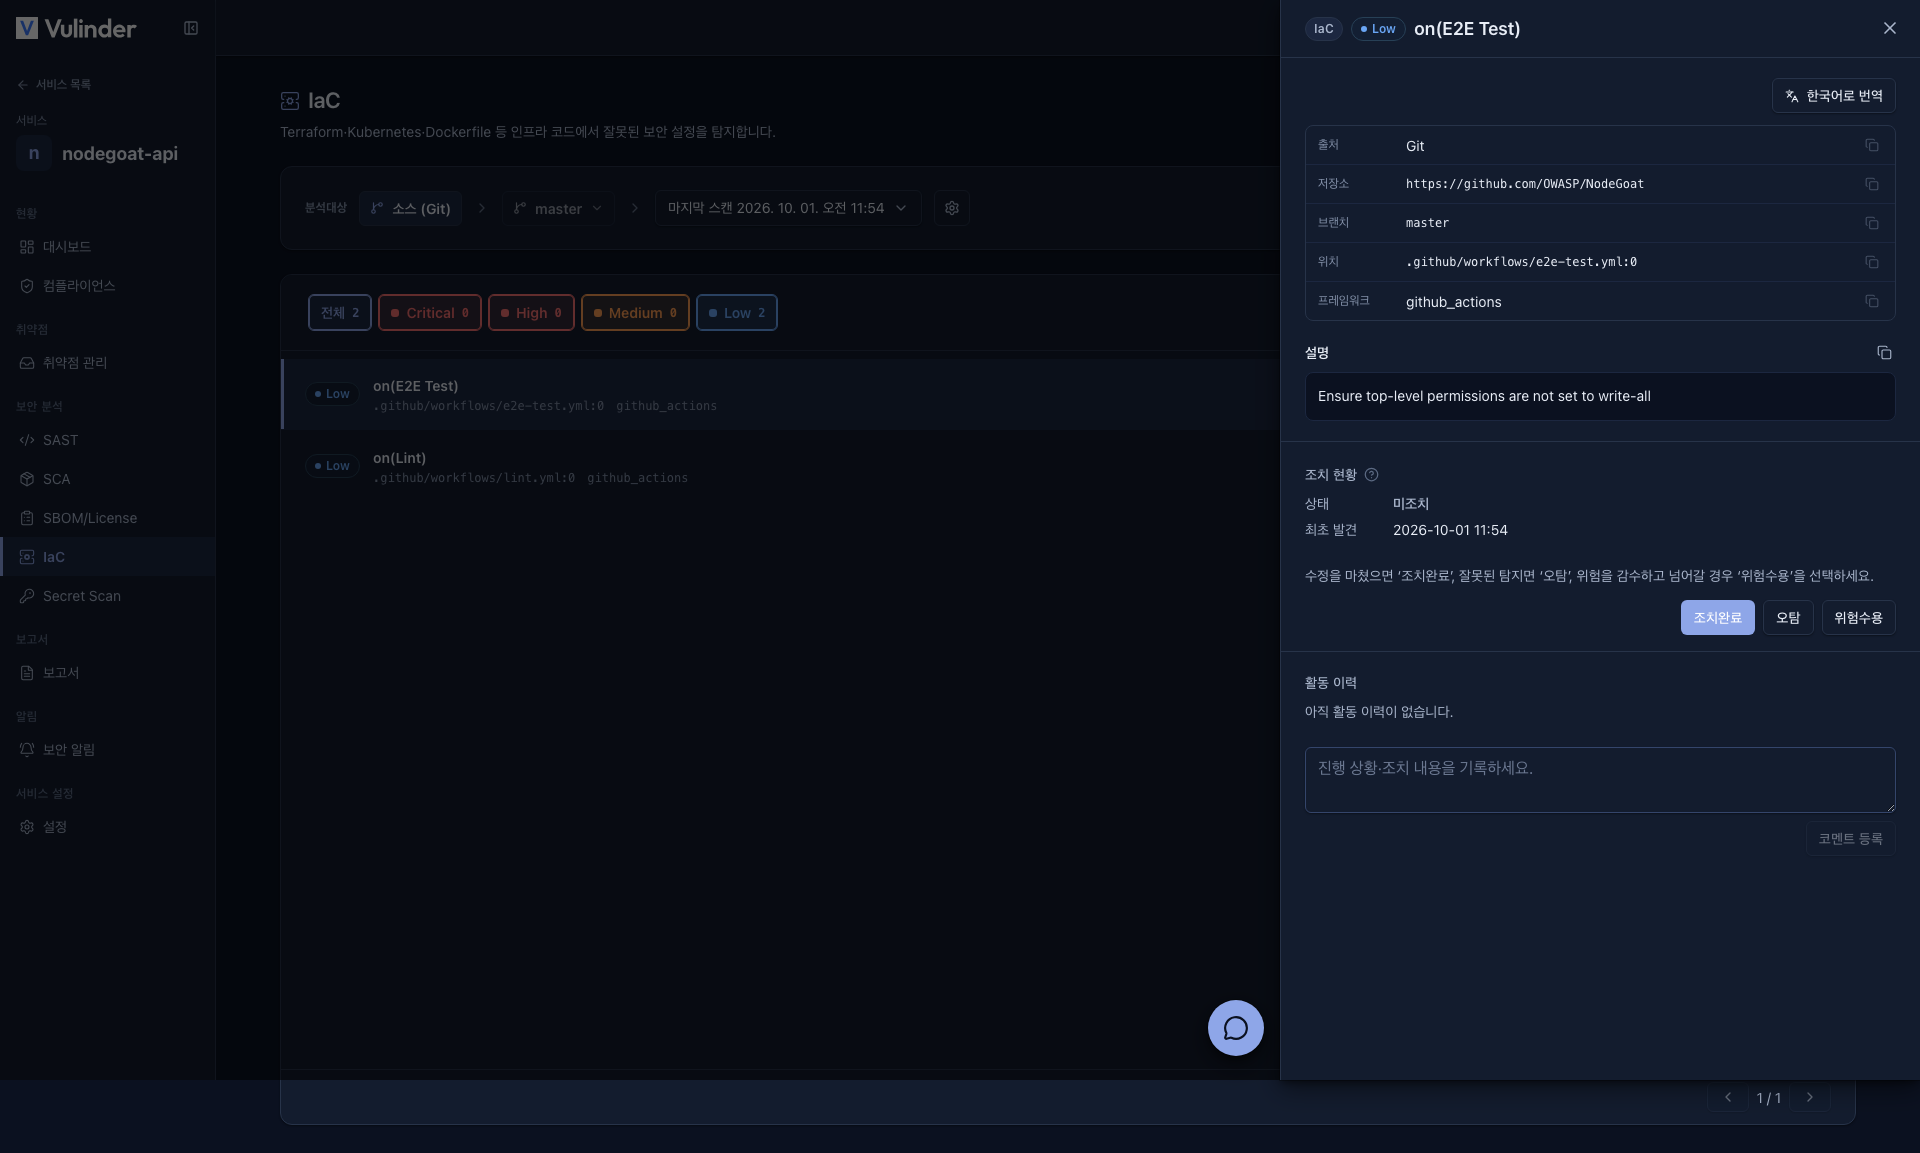
Handling results
- If a setting is intended per organization policy, mark it as accepted risk.
- Exceptions to a tool rule can be suppressed as false positives.
- IaC results are also mapped to Compliance standards.
IaC analysis looks at the code (definition files). The configuration of clusters / nodes actually in operation is checked by K8s cluster · CIS benchmark checks. The code may pass while the operational state has drifted, so the two are complementary.
Related documents
- K8s cluster · CIS benchmark : Actual state of clusters and nodes in operation
- Compliance : Standards mapping for configuration flaws
- Vulnerability Management : Review and handle findings