Compliance
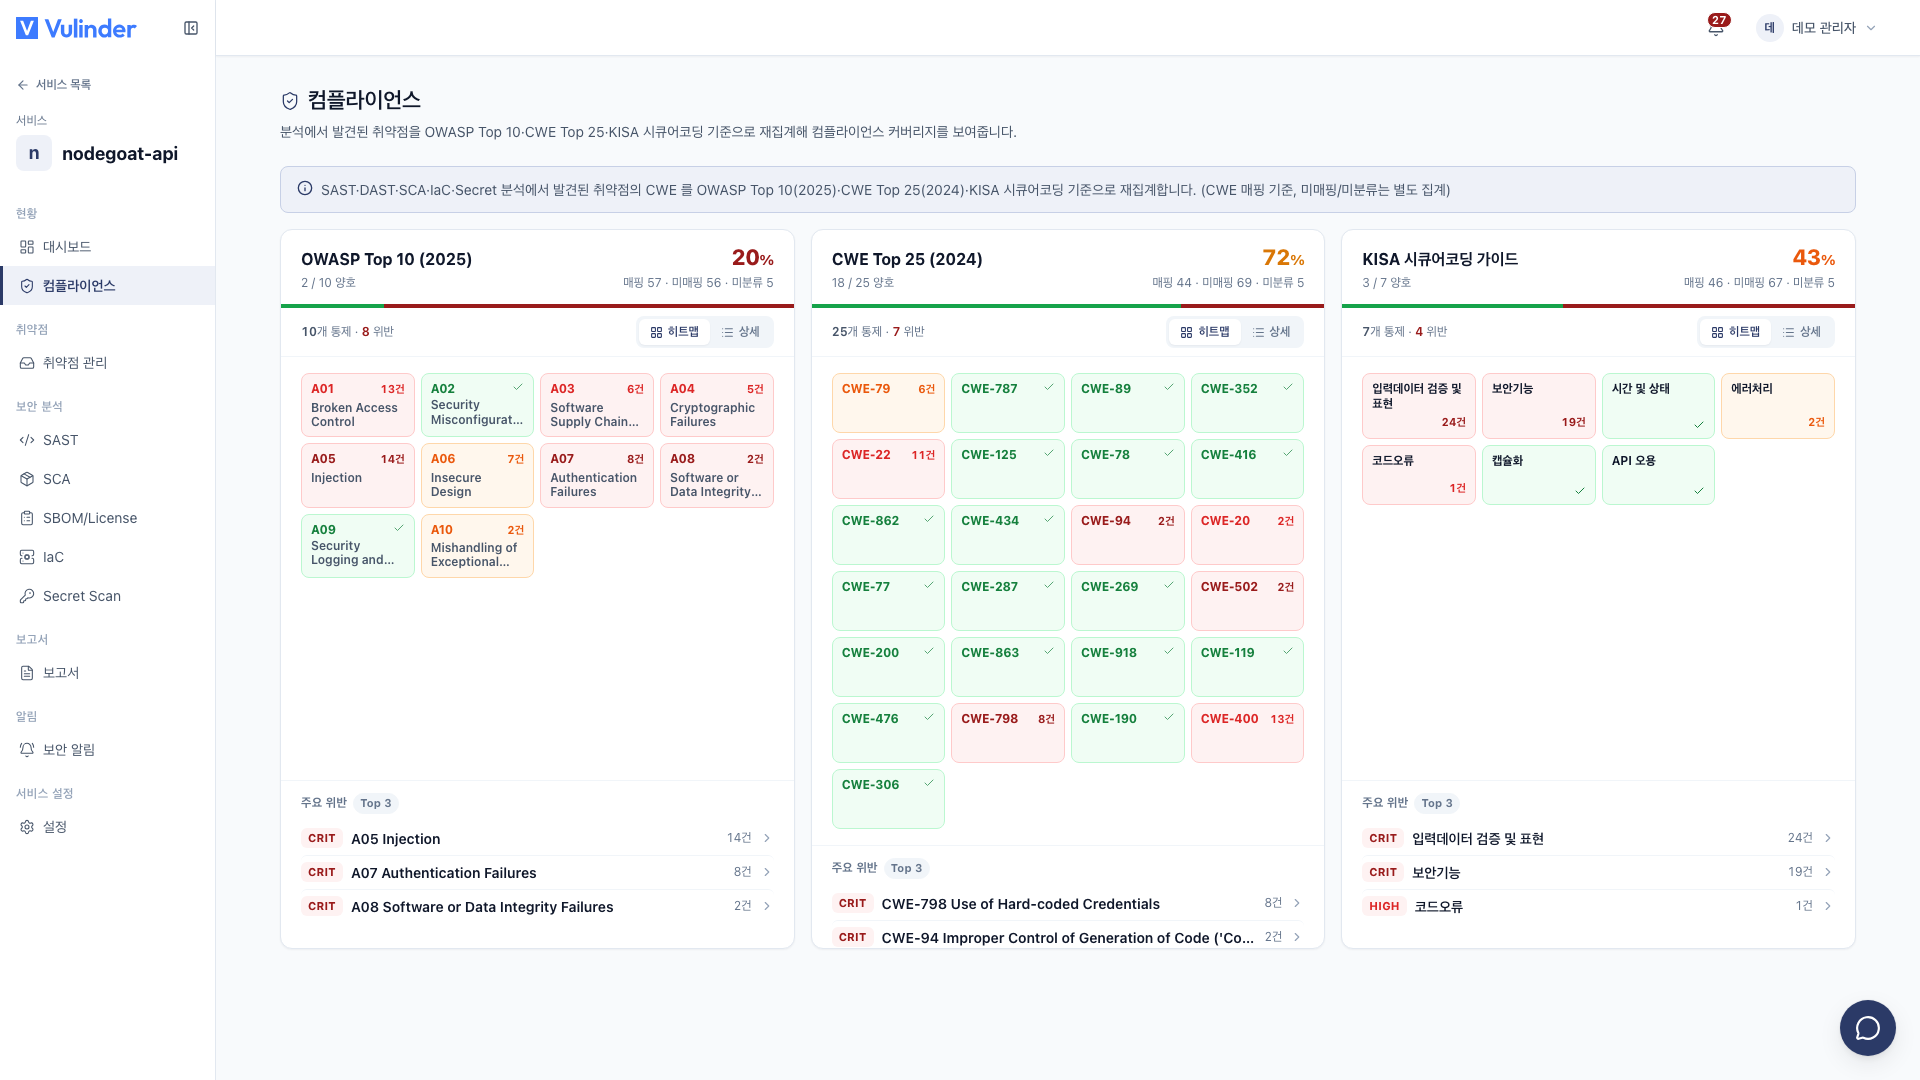
Maps found vulnerabilities to standard security baselines and shows the compliance status. Beyond individual findings, you can see at a glance "which standard you meet and how well", which is directly useful for audit response and priority decisions.
Supported standards
- OWASP Top 10 (2025)
- CWE Top 25 (2024)
- KISA secure coding guide
For server / host services, a CIS Kubernetes Benchmark card is also shown once a CIS check has run.
Coverage and drill-down
- Compliance percentage : Shows as a percentage how well you comply with each standard. Handling and cleaning up items in Vulnerability management is reflected in the figures.
- Drill-down : Click a failing control to expand the related findings in place, showing each item's analysis tool and source. Click an item in that list to go to the corresponding analysis screen.
Mapping basis
Compliance mapping is based on classification information such as the CWE of each finding. Items without classification information may not be mapped.
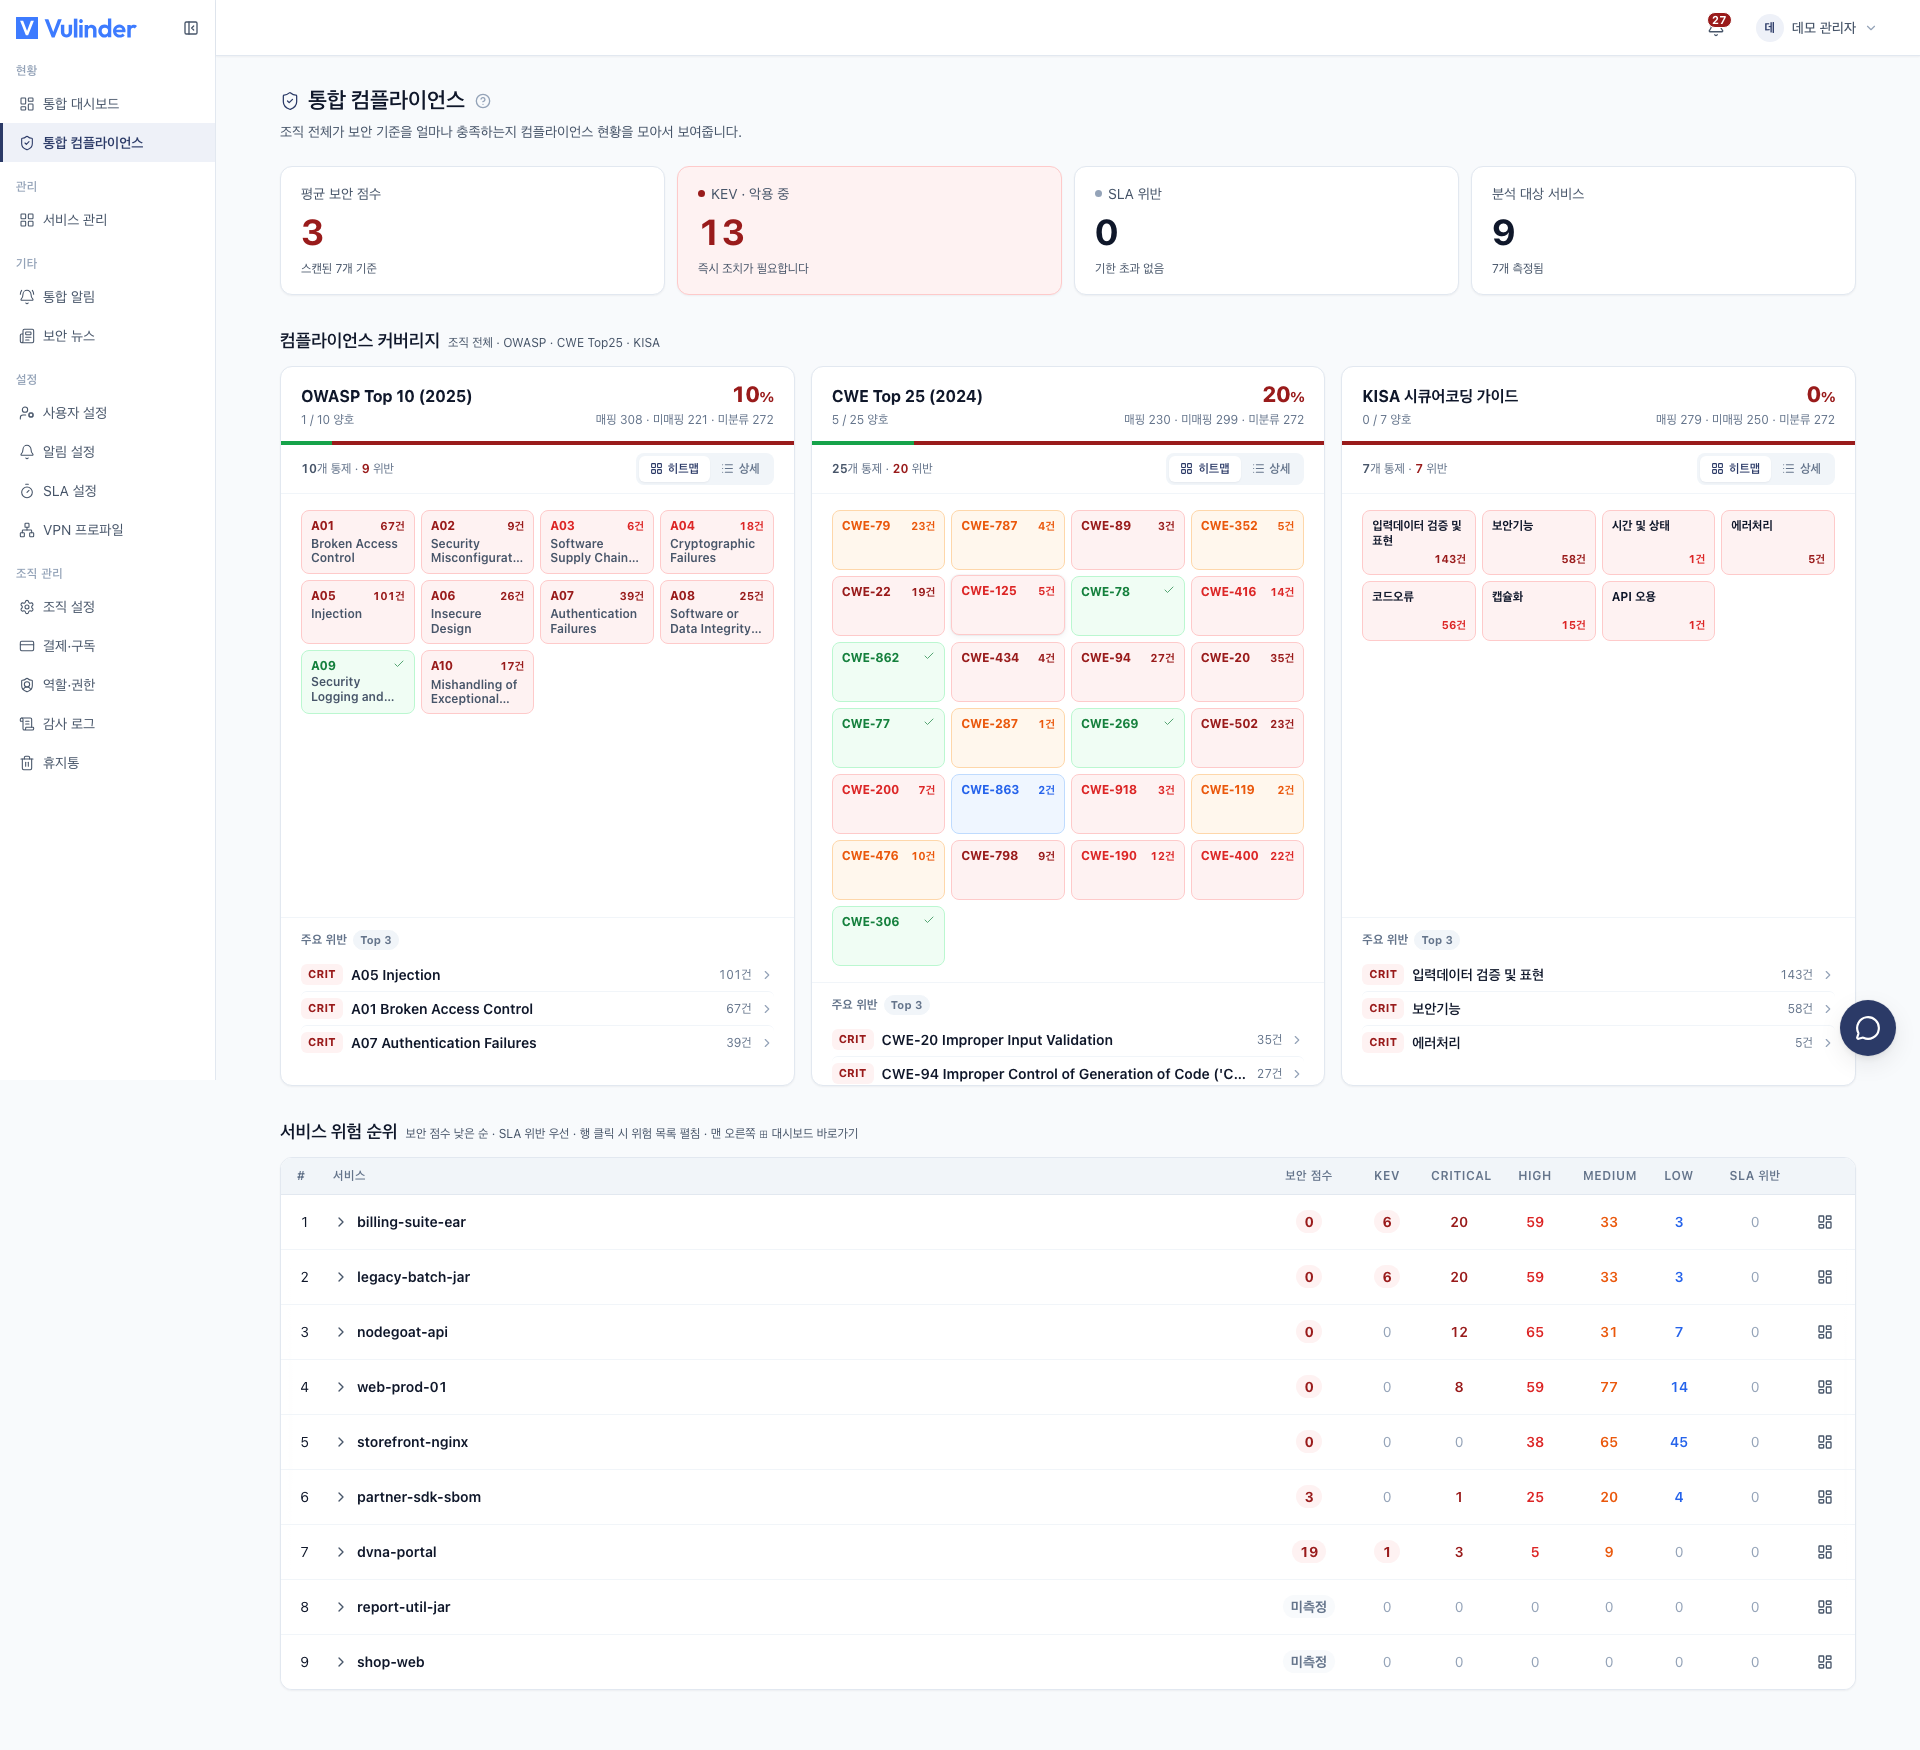
Organization-unified view
You can view the compliance of multiple services aggregated at the organization level. Deleted (trashed) services are excluded from the aggregate, so only currently operating services are accurately reflected.
Related documents
- Vulnerability Management : Handle non-compliant items
- Reports & VEX : Share compliance status as a report
- Dashboard : Confirm overall posture via the security score