Audit log
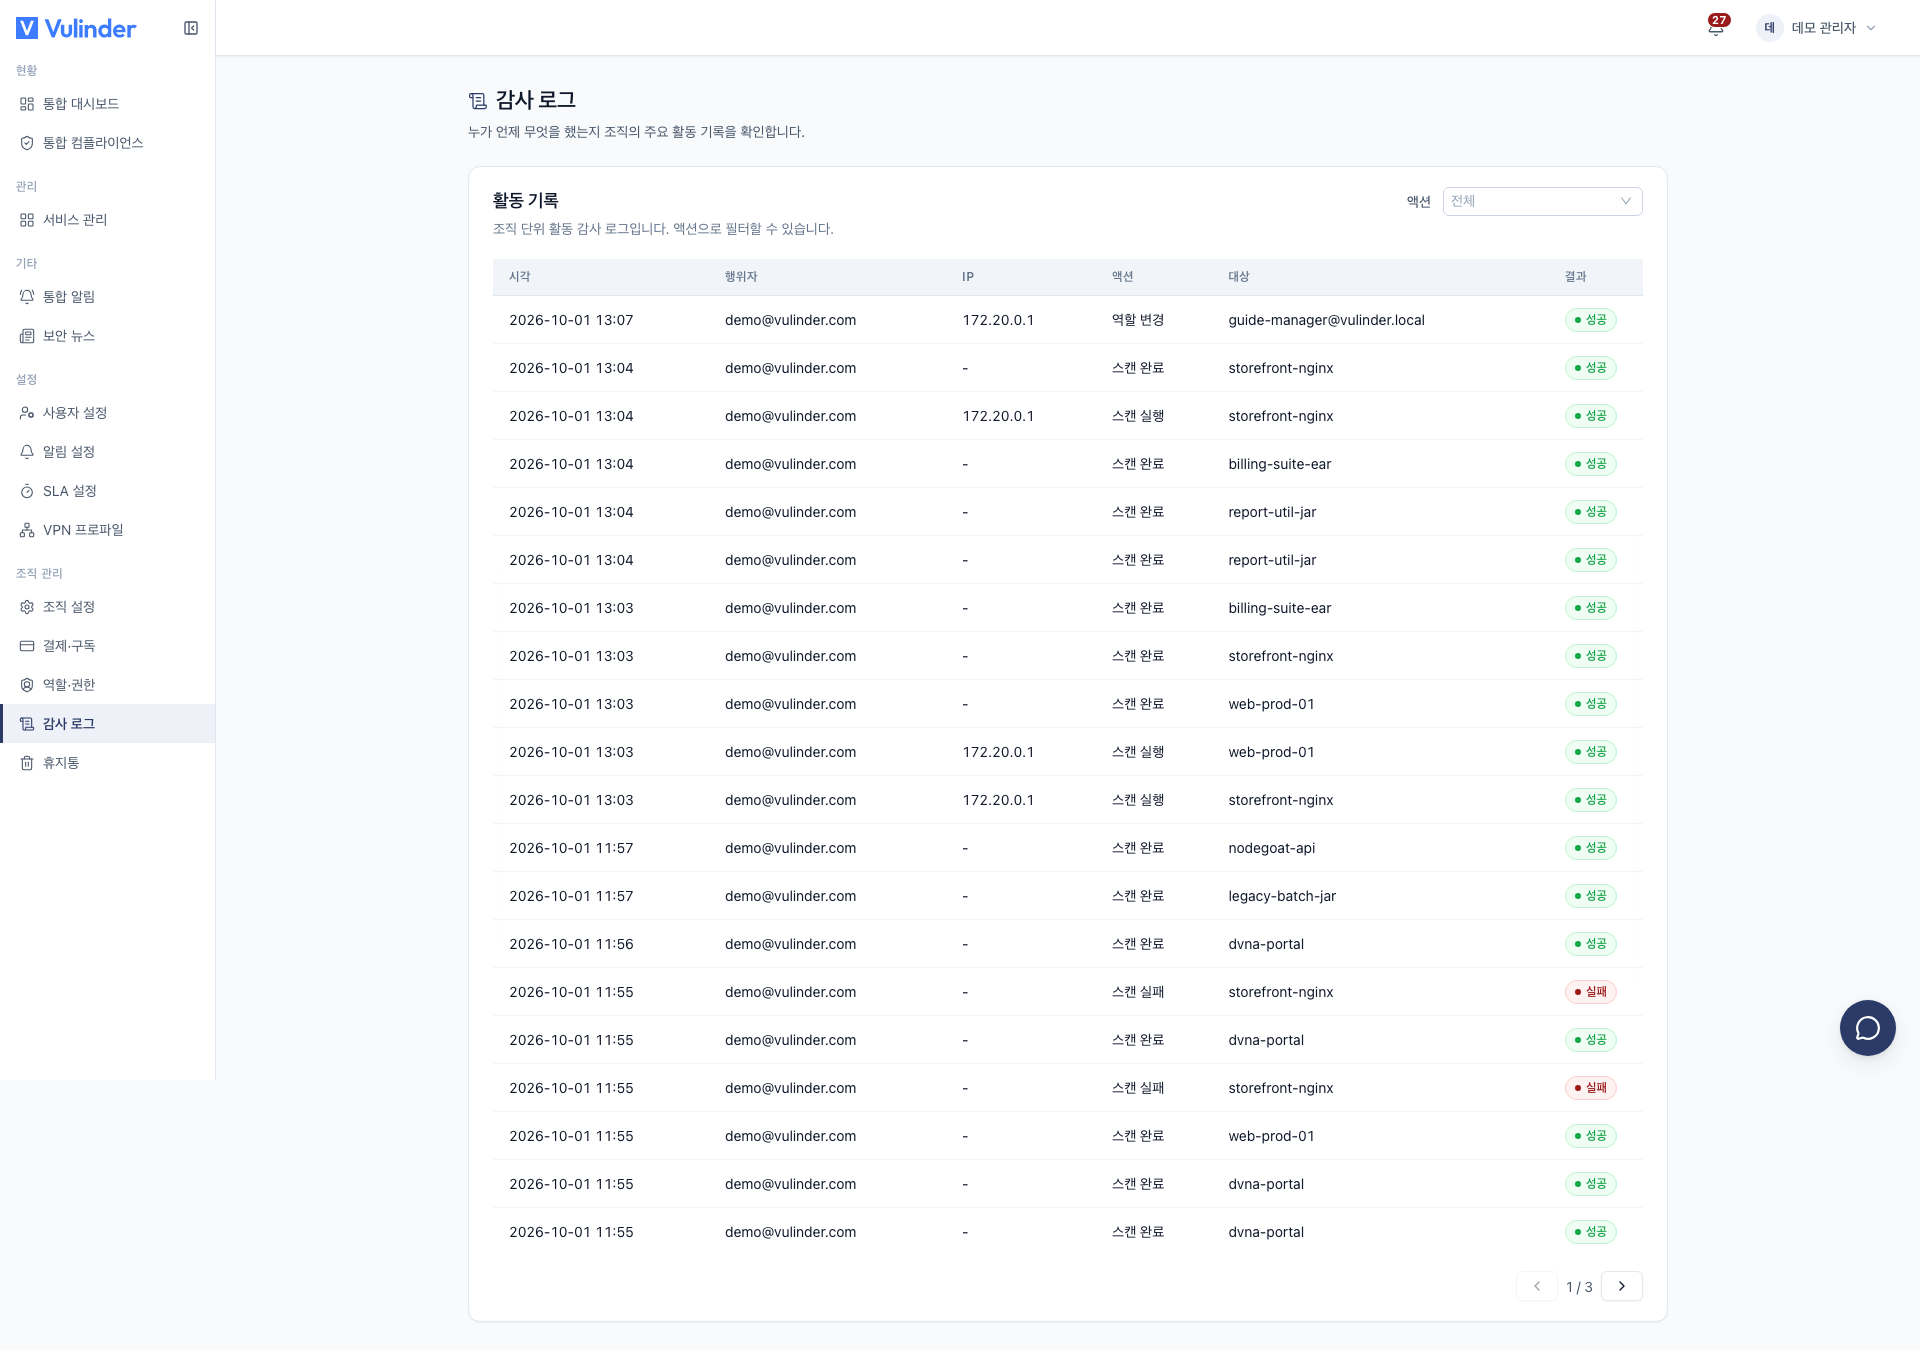
Being able to trace "who changed what and when" is what makes incident investigation and internal controls possible. Major actions in your organization are recorded together with the time, actor, and client IP, so you can check the exact history when you need it.
What is recorded
- Scan started/completed/failed
- Organization name changes, scan scope (K8s namespace) changes
- Member approval · rejection · role change · removal, leaving · closing the organization
- Service deletion · restore · permanent deletion
Each record includes the actor, the time, and the client IP address.
Scope
The audit log is isolated per organization. Admins and managers can view only their own organization's log under Organization > Audit log, filterable by action.
Related documents
- Members · Roles : Context behind role-change history
- Notification settings : Real-time notice of key events